

Security Summit 2025 (demo)
Thank you, Athens. Here is what we showed.
Two days, one attack path broken live on stage, and a room full of good questions.
Watch the talk
30 sec recording
- Conference centreAthens, Greece
- 11:30Talk · Main hall
Highlights
-

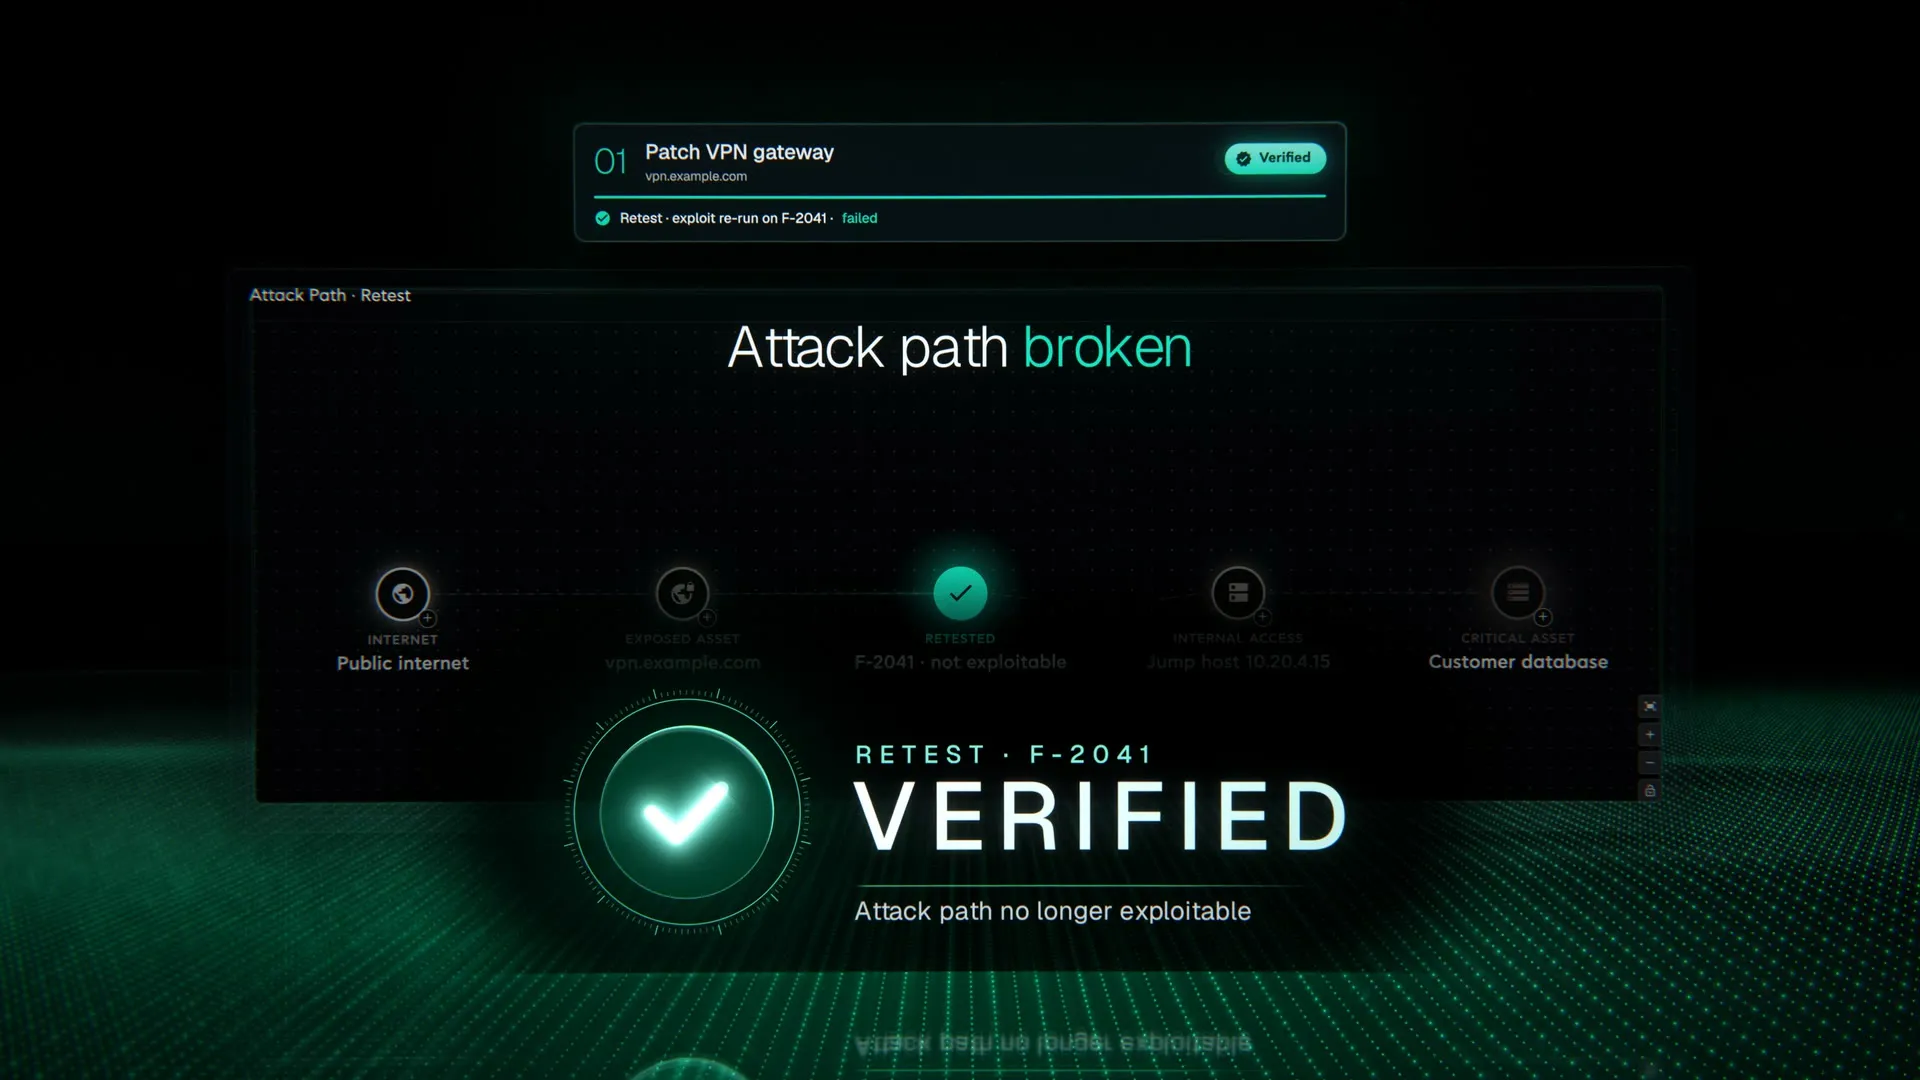
An attack path, broken on stage
From an exposed VPN gateway to the customer database, then the one fix that closed it.
-

Questions from the floor
Teams brought their own findings, and we ranked them live.
-

Between the sessions
Thirty-minute meetings, booked ahead on the event page.
More photos from Security Summit (demo)
3 photos · Select one to enlarge
If you missed it
From thousands of findings to the one fix that matters
Most teams have more findings than time. The talk showed how proving what is exploitable, and following the attack path to the assets that matter, turns that list into a short plan ranked by the risk each fix removes.
- Prove what an attacker can actually exploit before ranking anything.
- Follow the attack path to the asset that matters, not the scanner score.
- Fix the step that breaks the most paths first.
Why meet Mind The Hack
Exploit Validation
Proven risk, not theoretical findings. Every exposure is safely exploited and backed by proof-of-concept evidence.
Attack Path Analysis
See the chain. Break it once. How proven weaknesses connect into a path to your critical assets.
Contextual Risk Prioritization
Decisions that reduce risk. Exploitability, exposure and business context rank the few fixes that cut the most risk.

Request a demo
Thirty minutes on your own environment: what an attacker could exploit today, and the fixes that cut the most risk.
- EU-hosted
- ISO 27001 certified
- 30 minutes
What happens next
- We reply within one business day to agree a time that suits your team.
- Thirty minutes, live, on your own external perimeter. Nothing to install.
- You leave with the fix that matters: the one change that breaks the most attack paths.